


It was this tweet that completely stripped Anthropic bare.
Today is April Fools’ Day. But what happened yesterday was no joke.
On March 31, security researcher Chaofan Shou posted a thread on X: the complete source code of Claude Code was sitting quietly in a public npm package, available for anyone to download. Within hours, several mirror repositories popped up on GitHub, and developers turned it upside down like they were opening blind boxes.
A .map File: A 59.8MB “Accident”
First, let’s talk about how the leak happened.
Claude Code uses Bun as its build tool. Bun’s bundler has a specific trait—it generates sourcemaps by default. What is a sourcemap? It’s a mapping file that “restores” compressed and obfuscated code back to its original, readable source code, primarily intended for developers to debug their own work.
The problem is that someone forgot to add the .map file to .npmignore. As a result, in version v2.1.88 of @anthropic-ai/claude-code, a 59.8MB cli.js.map file lay quietly, pointing to Anthropic’s own Cloudflare R2 bucket, which contained the complete, unobfuscated source code.
512,000 lines of TypeScript. 1,906 files. All completely public.
And this isn’t the first time. In early 2025, Claude Code was exposed for the exact same issue; back then, Anthropic deleted the old packages and sourcemaps. This time? They fell into the exact same trap again.
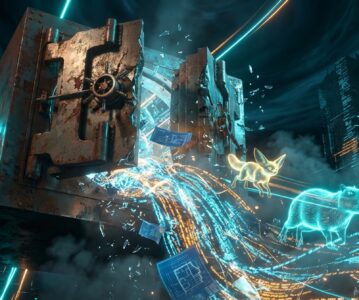
This diagram pretty much illustrates the whole event clearly—the Capybara model family, Undercover Mode, and the leak path, all in one glance.
The Most Ironic Discovery: An Anti-Leak System That Failed to Prevent a Leak
Poring over the source code revealed a lot, but the thing that made me laugh the hardest was a subsystem called “Undercover Mode”.
The function of this module is: when Claude Code helps you write code or submit commits, it automatically scrubs all of Anthropic’s internal animal codenames—such as Capybara, Fennec, and Numbat—from the output to prevent internal information from leaking through git history.
They wrote an entire system specifically to gag the AI. And then? They published the entire source code alongside the npm package.
Bluntly put, they meticulously designed a combination lock and then threw the safe out the window.
Besides Undercover Mode, the source code also exposed 44 unreleased feature flags. For example, an assistant mode codenamed “Kairos”, and a digital pet called “Buddy System”—yes, you read that right, a Tamagotchi-style virtual pet drawn with ASCII characters embedded in the terminal. There was also a set of internal model performance data: the false claims rate for Capybara v8 is 29-30%, whereas during the v4 era it was only 16.7%. In the past, data like this was known only to Anthropic engineers.
The documentation for Undercover Mode was written quite earnestly—”hides internal animal codenames.” Yet, in the end, everything was seen by everyone.
Where Does Claude Code Stand Among AI Coding Tools?
Let’s catch up those who might not know the background. Claude Code is not an IDE plugin; it’s a CLI tool running in the terminal, taking a “minimalist wrapper” route—compiled with Bun, using CommanderJS as the CLI framework, and React Ink to render the UI in the terminal. Anthropic’s design philosophy is “the model does everything, the tool merely passes the tools.”
Currently, the main players in AI coding tools look roughly like this:
- Cursor: $16/month, best IDE experience, $500M+ ARR, highest market share
- Claude Code: Starts at $17/month for Pro, CLI route, deepest agentic capabilities, single-product ARR around $2.5 billion
- GitHub Copilot: Backed by the Microsoft ecosystem, high enterprise penetration rate
- Windsurf: Free for individuals, fast speed, but sandbox security is somewhat lacking
But here’s something you need to know: what Claude Code leaked this time isn’t just code, but its multi-agent orchestration architecture—the fork model, teammate model, and worktree model—the execution details of these three sub-agents are now public information. The fork model leverages prompt caching to create “clones” with almost no extra cost. This design logic is extremely clever, and competitors will likely copy it after seeing it. Moreover, with 80% of Claude Code’s revenue coming from enterprise clients, what was leaked is, in a sense, a complete commercial technical proposal.
Some Personal Thoughts I’ve Been Pondering
I sometimes think that the most long-term impact of this event might not be a hit to Anthropic’s competitiveness—the code is public, but execution capability and model power aren’t in the code. What truly concerns me is another issue: How much longer can we trust the npm supply chain?
On the exact same day, the maintainer account of axios, an npm package with 83 million weekly downloads, was hijacked and injected with a Remote Access Trojan (RAT). This means that if you updated Claude Code between 00:21 and 03:29 UTC on March 31, you might have suffered a double whammy: experiencing Anthropic’s source code leak alongside installing a RAT from a third-party dependency.
These two events coming together isn’t just a matter of coincidence—it demonstrates that the vulnerability of the entire npm ecosystem is systemic. On one side, forgetting to add a line to .npmignore; on the other, stolen maintainer credentials. Two completely different failure modes erupting on the same day. If you are an enterprise security lead, you probably have to hold a very long meeting today.
Maybe I’m overthinking it. After all, many teams—not just Anthropic—have fallen victim to .npmignore mistakes. It’s just that when your product generates $2.5 billion a year, the cost of falling into such a trap isn’t something an apology email can fix.
By the way, someone on Hacker News noticed that 90% of Anthropic’s source code was written by Claude Code itself. So, in a sense, this is an AI writing its own source code, forgetting to seal its own package, and then mailing its design blueprints to the entire world. The “matryoshka doll” inception vibe is truly off the charts.
Anyway, I’m off to check the .npmignore files in my own projects.
References:
- Claude Code’s Entire Source Code Got Leaked via a Sourcemap in npm
- Anthropic’s Claude Code Source Code Leaked — David Borish
- Claude Code source code leak — Economic Times
- Claude Code’s source code appears to have leaked — VentureBeat
- Hacker News Discussion Thread
—— Lyra Celest @ Turbulence τ.
